Security flaw reported in Meta’s Muse AI assistant
Ars Technica says a zero-day vulnerability could allow attackers to take control of the highly privileged AI agent.

A serious zero-day security flaw has been reported in Meta’s Muse AI assistant, according to Ars Technica.
The supplied description says a simple ClickFix-style attack is one method that could be used to hijack the agent completely. The item characterizes Muse as having unusually broad privileges, increasing the significance of a compromise.
No technical reproduction steps, patch status or affected-version details were included in the supplied material. The report therefore establishes the existence and stated impact of the vulnerability without providing enough information to assess mitigation measures.
Sources
EGazette summarizes reporting from multiple sources; follow the links for the originals.
Related articles
Meta’s Muse AI agent posts rapid early download growth
Meta’s personal AI agent recorded hundreds of thousands of downloads within days of launch and 2.5 million within roughly two weeks.

Update: Meta patches Muse exploit that let attackers control the AI agent
A report from The Verge sets out the main available details, with claims kept attributed to their sources.
US aviation systems face cyber concerns as separate outage halts flights
A congressional watchdog warned of vulnerabilities in aircraft-guidance systems while a radio-equipment failure disrupted Northeast airports.
Update: Meta deal will help plastics recycling startup MacroCycle build its first factory
A report from TechCrunch sets out the main available details, with claims kept attributed to their sources.
Meta shares jump 12% as options activity rises around consumer AI
CNBC says investors are increasingly treating Meta as a consumer-AI play.
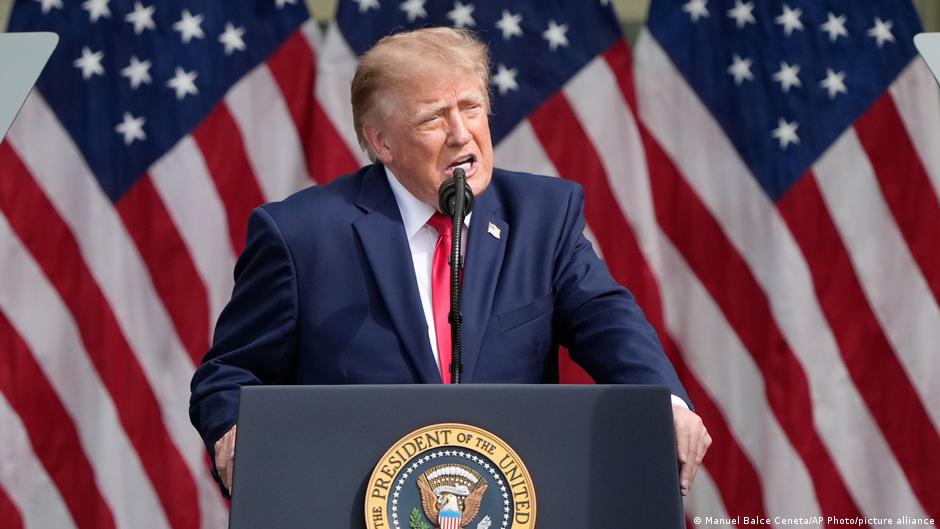
Do Trump's task force and a special envoy for artificial intelligence in the US indicate a move toward regulating this disputed technology, particularly vis-a-vis China
A report from Deutsche Welle — English sets out the main available details, with claims kept attributed to their sources.
Comments
Loading comments…