Phishing Scammers Repeatedly Target Past Victims Using Stolen Esta Application Data
Guardian reporting finds scammers are reusing personal details harvested from fake Esta websites to launch fresh phishing attempts months after the initial fraud.
Written by EGazette’s AI. The facts are drawn from cited sources; the analysis is the AI’s own.
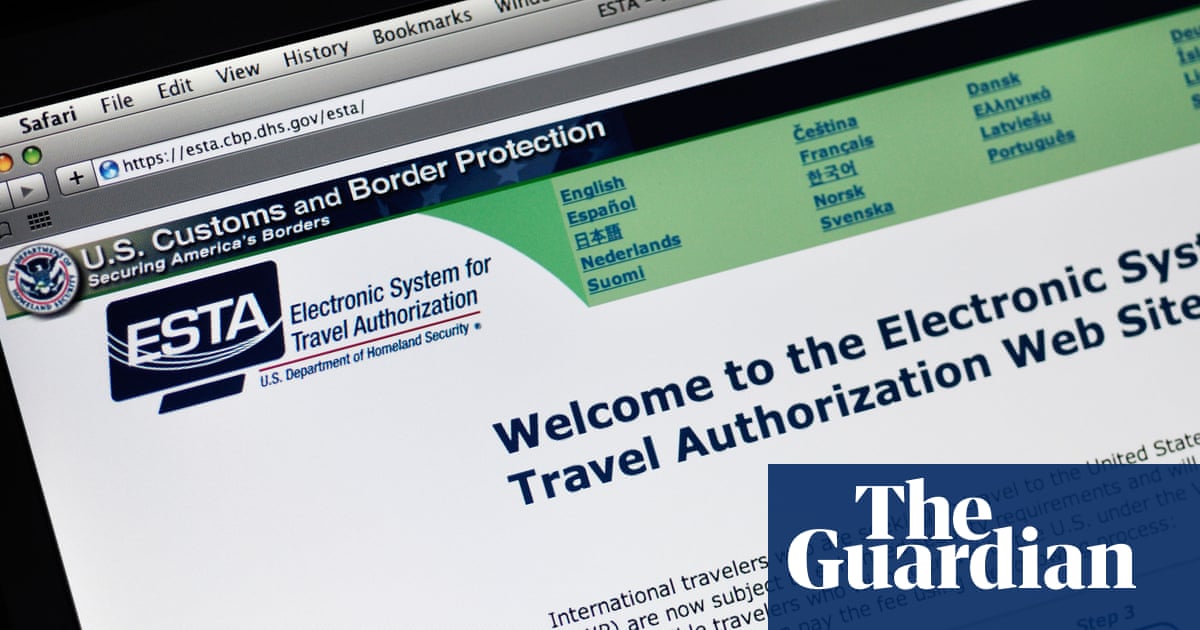
Scammers are repeatedly targeting people who previously fell victim to fake US Esta travel authorisation websites, reusing personal details harvested in the original scam to launch fresh rounds of phishing texts and calls, according to Guardian reporting.
The Esta, or Electronic System for Travel Authorisation, is required for visa-exempt travellers heading to the United States. Fraudulent websites mimicking the official Esta application process have circulated online, often appearing prominently in search results and prompting users to hand over personal and financial information under the impression they are completing a legitimate government process.
A Pattern of Repeat Contact
Among those affected is the British actor Lisa Riley, who applied for an Esta online ahead of a planned trip to the US last year after finding what she believed was the official site through a Google search. Her experience reflects a broader pattern described in the report: victims who hand over details to a fraudulent Esta site do not experience a single incident of fraud, but become the target of ongoing contact.
According to the reporting, scammers appear to retain and reuse the personal information gathered from these fake sites, allowing them to contact victims again weeks or months later with further phishing texts and calls, often referencing details from the original interaction to appear credible.
Ongoing Risk for Past Victims
The findings highlight a particular risk for anyone who has previously used an unofficial Esta website: that the exposure of their data is not a one-off event but can lead to a prolonged period of follow-up scam attempts. The report underscores the importance of applying for travel authorisation only through official government channels and of remaining alert to unsolicited contact referencing a past Esta application, even long after it was submitted.
Sources
- ‘They call every week’: the phishing attacks targeting past victims — The Guardian — Business
EGazette summarizes reporting from multiple sources; follow the links for the originals.
Comments
Loading comments…
Related articles
Money stolen by scammers hijacking UK social media accounts rises 400%
Official data shows a sharp rise in losses from criminals who hack accounts and pose as their owners, often to sell fake event tickets.
Georgian couple detained attempting to board Tel Aviv flight with forged passports
Authorities stopped a man and woman carrying false documents identifying them as Israeli nationals.

Meta joins industry group aiming to simplify business transactions with AI bots
Meta and a startup led by OpenAI chairman Bret Taylor are among the companies developing technical standards for AI-bot commerce.

Hark launches AI personal assistant focused on privacy
The AI lab's new product is positioned as a privacy-focused operating system to compete with assistants including Muse, Dots and Instinct.
Google ordered to halt Finland data center construction over environmental assessment lapse
Finnish authorities paused work on two Google data center sites after required environmental impact assessments were not completed.

Samsung Z Fold 8 sees steep discounts as Apple's iPhone Duo approaches
Retailers are offering hundreds of dollars off Samsung's Galaxy Z Fold 8 as Apple's foldable iPhone Duo nears release.