Report: Suspected Chinese-Speaking Hacker Used AI to Breach South Korean Banks
Cybersecurity firm CrowdStrike links the attacks to a Chinese-developed hacking tool and says the stolen data may have been intended for sale.
Written by EGazette’s AI. The facts are drawn from cited sources; the analysis is the AI’s own.
A suspected Chinese-speaking hacker used artificial intelligence tools to breach South Korean banks, according to a report from the U.S. cybersecurity firm CrowdStrike, which linked the attacks to a Chinese-developed hacking tool.
CrowdStrike's findings indicate that the data obtained in the breaches may have been targeted with the intent of selling it, suggesting a financially motivated operation rather than one aimed purely at disruption or espionage.
The use of AI in the intrusions reflects a broader trend that cybersecurity researchers have flagged in recent years, in which attackers increasingly incorporate automated and AI-assisted techniques into hacking operations to improve their effectiveness or evade detection.
Details regarding the specific banks affected, the scale of the breach, and the exact nature of the data obtained were not fully specified in the available reporting. CrowdStrike's attribution of the attacks to a Chinese-developed tool and a Chinese-speaking actor points to the firm's technical analysis of the malware or infrastructure involved, though attribution in cybersecurity incidents often carries inherent uncertainty.
The report adds to a growing body of findings from security researchers tracking financially motivated hacking campaigns against financial institutions across Asia, with South Korean banks representing the latest reported target in this pattern of activity.
Sources
- Suspected Chinese-speaking hacker uses AI to breach South Korean banks: Report — Anadolu Agency (Turkey)
EGazette summarizes reporting from multiple sources; follow the links for the originals.
Comments
Loading comments…
Related articles
OpenAI used its own AI to draft email disclosing hack of Australian government sites, report says
The Guardian reports the admission follows testimony in which an OpenAI executive said he did not believe AI had written the message.

Analyst Dan Ives Says AI Buildout Is Only in Its 'Third Inning,' Names Top Picks
Wedbush analyst Dan Ives says the artificial intelligence investment cycle still has a long way to run and argues AI's growing role in cybersecurity is a net positive for the sector.
Cramer previews the week ahead as bank and chipmaker earnings test the AI trade
CNBC's Jim Cramer says upcoming earnings reports will offer a clearer read on corporate performance and the strength of the AI-driven rally.

Samsung Forecasts Record Quarterly Profit of $80 Billion Amid AI Chip Demand
The company's preliminary earnings put operating profit above 100 trillion won for the first time, according to CNBC.

South Korea Signals Military Exemption Cuts for Gold Medallists After Asian Games Backlash
The move follows public backlash over comments made by athletes at the Asian Games, according to a report from Al Jazeera.
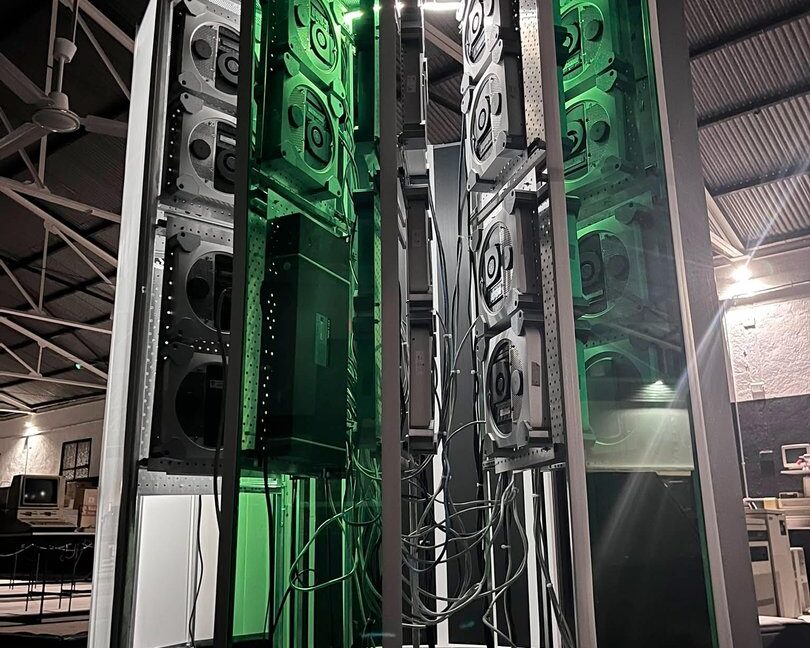
A Cray-1 supercomputer replica built from 30 "obsolete" Mac Minis
A retro-styled upcycling project at Spain's Museo de Historia de la Computación recreates the classic machine's iconic look.